Built to protect patient photos and records.
CureCast combines seven security controls to manage who accesses patient information, what activity is recorded, and how data is protected at rest and in transit.
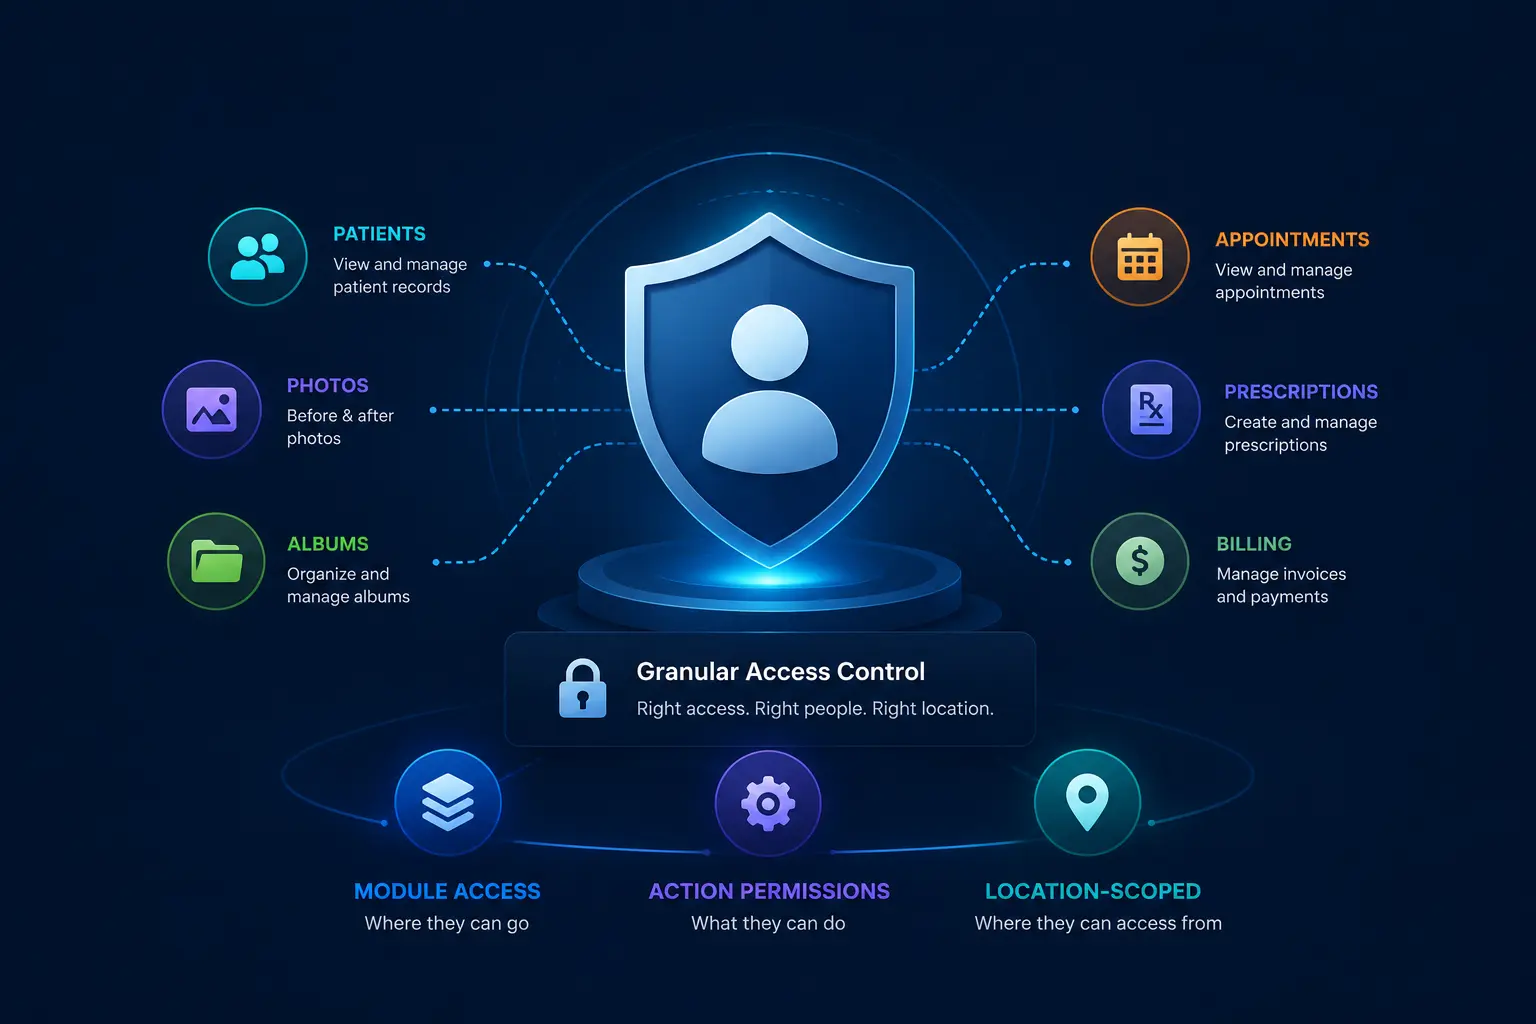
- Staff Access Control: who can access what
- Audit Trail : What activity is recorded
- Device Management : Which devices have CureCast access
- Session Timeout : How inactive sessions are handled
- Encryption : How patient records and clinical photos are protected
- Confidential Patient : invisible to unauthorised staff
- Multi-Clinic : How access stays scoped to a single clinic location
Good to know: CureCast security features support a practice's privacy and security workflow. They do not replace the practice's own policies, risk assessment, staff training, patient-consent process, device-security controls, or legal obligations.
How CureCast Protects Patient Information
Each control is explained in detail on its own page. Together they cover who has access, what gets recorded, which devices are trusted, how long a session stays open, how data is protected while it’s stored and moved, which individual patients need an extra layer of privacy, and how access stays scoped to a single clinic.
Beyond the Software
Security and compliance involve more than individual software features. Practices also need policies and procedures for access reviews, patient-photo consent, device security, incident response, staff offboarding, and applicable privacy laws.
What Is HIPAA Compliance?
An ongoing program of policies, procedures, risk analysis, training,
and technical safeguards. There is no single government-issued HIPAA
certificate that makes a platform or practice compliant.
Who Should Have Access to Patient Photos?
Not every staff member needs access to every record. Module-level and
action-level permissions let a practice match access to actual job
responsibilities.
What Should a Healthcare Audit Trail Record?
Patient-record views, file downloads, shares, failed logins, consent
activity, exports, device context, and timestamps, though a log record
activity, it doesn’t decide whether access was appropriate.
What Should a Practice Do After a Lost Device?
Review the device record, end the CureCast session, preserve available
audit activity, and follow the practice’s broader incident-response
procedure.
What Is Automatic Session Timeout?
An inactive session ends after a defined period, 2 hours on desktop,
4 hours on supported mobile with a warning before logout and a
required sign-in.
How Should Practices Protect Clinical Photos?
Staff permissions, download and sharing controls, consent management,
device and session security, staff training, and lost-device procedures
together, not any one alone.
What Is Confidential Patient Access?
A per-patient privacy setting. A confidential patient doesn’t appear in
search, lists, or galleries for staff without confidential patient
access, with no locked-record indicator and no trace they exist for that
person.
Does Each Clinic Location Have Separate Data?
Yes. Each location is its own CureCast account. A staff member at one
clinic can’t see another clinic’s patients or photos unless separately
given access to that account too.
See How CureCast Fits Your Practice
Discuss how CureCast fits into your clinical photo workflow, from capturing and organizing patient photos to securely managing them across your practice.
Prefer email? [email protected]